
• Latest
  • Trending
  • All
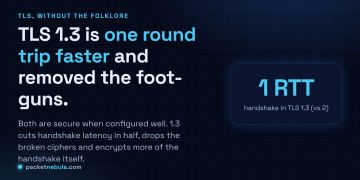
Answer card: TLS 1.3 is one round trip faster than TLS 1.2 and removed the broken options; both are secure when configured well.

TLS 1.2 vs TLS 1.3: what changed and what to run in 2026

12 June 2026
Answer card stating that OpenAI released the Agents API in public beta on 10 September 2026 with no separate fee, billed through model tokens, tool calls and hosted sandbox time, with a choice of OpenAI hosted, self hosted or partner sandboxes, US only data residency and no Zero Data Retention support.

OpenAI’s Agents API has no fee, no ZDR and a one hour sandbox clock

14 September 2026
Answer card: Sakana Fugu Max at $2 and $6 per million tokens, Fugu Ultra v2 unchanged at $5 and $30, and Sakana saying Ultra v2 scores without Fable 5 or GPT-6 Astra in its pool.

Fugu Max costs $2 and $6 while Fugu Ultra v2 runs without Fable 5

13 September 2026
Answer card stating that DeepSeek released DeepSeek-V4.1-Flash on 10 September 2026 as a 552 billion parameter mixture of experts model with a new causal encoder decoder architecture that activates 8 billion parameters on input and 16 billion on output, with native vision, a one million token context and MIT licensed weights, that the API model name is now deepseek-flash at 0.15 dollars per million input tokens and 0.60 dollars per million output tokens off peak, and that DeepSeek announced V4 Pro would be routed to V4.1-Flash from 14 September and reversed that on 11 September.

DeepSeek V4.1-Flash arrived, and the V4 Pro retirement lasted a day

12 September 2026
Answer card stating that Cognition released SWE-2 on 10 September 2026, a coding model post-trained from Kimi K3, scoring 50.0 percent on FrontierCode 1.1 Main against 50.9 percent for Claude Fable 5.1 and 27.3 percent on Terminal-Bench 4 against 55.8 percent, available only inside Devin.

SWE-2 trails Fable 5.1 by one point, and by 28 on Terminal-Bench 4

11 September 2026
Answer card for Meta Muse, free to 100 million tokens a week then $20 a month, launched 8 September 2026 for United States adults only, running in a dedicated per user virtual machine.

Does Meta Muse do enough to earn your inbox and a card on file?

9 September 2026
Answer card stating that the public download pages for the VMware Virtual Disk Development Kit on developer.broadcom.com began returning 404 errors on 25 August 2026 with no announcement or deprecation notice, that Broadcom support tells customers the kit is no longer available for use or download, and that release lines 7.0.3.1, 8.x and 9.x are all affected.

Broadcom pulled VDDK 8.0 and 9.0, and the 404 is the only notice

8 September 2026
Answer card stating that OpenAI published its research acceleration measurements on 6 September 2026, that as of mid August 2026 its research organisation logged 3.1 agent workdays of coding agent runtime for every workday of human labour normalised to a standard eight hour day, and that OpenAI states this should not be read as a 3.1 times productivity gain because it measures runtime rather than delivered output.

OpenAI’s 3.1 agent-workdays per human day is not a 3.1x gain

7 September 2026
Answer card stating that Mullvad announced on 3 September 2026 that it is shutting down its public encrypted domain name system servers on 2 November 2026 and sponsoring the Quad9 Foundation instead, with 194.242.2.2 and its five sibling addresses all going away, and virtual private network customers unaffected.

Mullvad’s DNS servers go dark on 2 November, and Quad9 blocks no ads

5 September 2026
OpenAI announcement image for GPT-6 Astra, a spiral galaxy of white, blue and amber points of light curling around a bright core on a near black star field.

GPT-6 Astra lists at $10 and $50, 2.5x what GPT-5.6 Sol costs

6 September 2026
Google's official announcement image for the release, reading Introducing Gemini 3.8 Flash and 3.8 Flash Cyber in black type over a pale blue background with a blurred white chevron and the four colour Gemini spark below.

Gemini 3.8 Flash keeps the price and the 1 January cliff

3 September 2026
Answer card stating that Anthropic announced Enterprise Frontier Safeguards on 1 September 2026, that activity data used for misuse monitoring moves into cloud storage the customer controls under the customer own encryption keys, that Anthropic charges nothing for the feature while the cloud provider bills storage and egress, and that the phased rollout starts later in autumn 2026 with interim zero data retention on Fable 5 and Fable 5.1 for eligible customers.

Anthropic moves retention into your own cloud, for 30 days

3 September 2026
Official Google diagram of a client connection in three numbered steps: a DNS lookup with a query and an address, a TLS ClientHello and ServerHello, then a content exchange with a website. A callout on the DNS step reads 25% of global web traffic is now protected by encrypted DNS, and a callout beside an Android phone on the ClientHello step reads Android 17 supports ECH GREASE by default.

Android 17 hides the SNI, not your DNS or destination

3 September 2026
  • About
  • Contact
  • Privacy
  • Legal
Tuesday, September 15, 2026
  • Login
Packet Nebula
  • Home
  • Articles
    • Security
    • Network
    • Dev
    • Sysadmin
    • SEO
    • Email & DNS
  • Tools
    • Network tools: free, fast, no signup
    • Security tools: free, fast, no signup
    • Developer tools: free, fast, no signup
    • Sysadmin tools: free, fast, no signup
    • SEO tools: free, fast, no signup
    • Email & DNS tools: free, fast, no signup
  • Download
  • About
No Result
View All Result
Packet Nebula
No Result
View All Result
Home Security

TLS 1.2 vs TLS 1.3: what changed and what to run in 2026

by stephane
12 June 2026
in Security
0
Answer card: TLS 1.3 is one round trip faster than TLS 1.2 and removed the broken options; both are secure when configured well.
498
SHARES
1.4k
VIEWS
Share on FacebookShare on Twitter

You upgrade nginx, point a checker at the host, and half your endpoints still answer TLS 1.2. Does that matter? Mostly no, and here's the short version: TLS 1.3 changed two things, the handshake dropped from two round trips to one so every new HTTPS connection starts faster, and the protocol deleted every cryptographic option that had ever gone wrong, so a careless config can't pick something broken anymore. What people miss is that TLS 1.2 isn't insecure, and you'll keep it as a fallback rather than rip it out. Both versions hold up fine when set up properly. We'll walk through where the speed actually comes from, the long list of what 1.3 removed and why, how post-quantum key exchange already rides on top of it, and exactly what to run on your servers in 2026.

The short answer

TLS 1.3 does two things to its predecessor: it cuts the handshake from two round trips to one, and it deletes every cryptographic option that ever went wrong, RSA key exchange and CBC ciphers included. Run 1.3 preferred with 1.2 as the compatibility floor; refuse everything older.
1 RTTTLS 1.3 handshake (1.2 needs 2)
5cipher suites left in 1.3
2018RFC 8446 published
Answer card stating TLS 1.3 is one round trip faster than TLS 1.2 and removed the broken options, with both secure when configured well.
The verdict up front. The interesting part is why those two changes were possible at once.

One round trip instead of two

A TLS 1.2 handshake is a four-flight conversation: the client offers its capabilities, the server picks and sends its certificate, the client ships key material and confirms, the server confirms back. Two full round trips before the first byte of your actual page moves. At 30 ms of latency, fine. At 150 ms on a phone, the handshake alone eats nearly a third of a second.

TLS 1.3, standardized as RFC 8446 in 2018, collapses that. The client guesses the key exchange group (it guesses right essentially always, since everyone uses x25519) and ships its key share inside the very first message. The server answers with everything at once, key share and certificate together. One round trip. Done. Resumed connections can go further with 0-RTT, sending data in flight zero, replay caveats included.

TLS 1.2: 2 round trips

ClientHello
ServerHello + Certificate
Key exchange + Finished
Finished

data starts here

clientserver

TLS 1.3: 1 round trip

ClientHello + key share
ServerHello + cert + Finished

data starts here

(0-RTT possible on resumption)

clientserver
The same job in half the conversation. The saving repeats on every new connection.

The great deletion

The speed got the headlines. The security story is the list of things TLS 1.3 removed. Static RSA key exchange: gone, so a stolen server key no longer decrypts past recorded traffic, and forward secrecy becomes mandatory instead of optional. CBC-mode ciphers with their padding oracle attacks (BEAST, Lucky13, POODLE’s cousins): gone. So are RC4, SHA-1 in signatures, compression (CRIME) and renegotiation, the source of a whole attack family.

What survives is a short list of five AEAD cipher suites, all AES-GCM and ChaCha20-Poly1305 variants, every one of them respectable. That’s the deeper design shift. TLS 1.2 was a menu where a sloppy administrator could still order something poisonous in 2026; TLS 1.3 took the poison off the menu. A whole genre of audit finding, the weak cipher suite, simply can’t exist on a 1.3-only endpoint.

The protocol also encrypts most of its own handshake, certificate included. Anyone watching the wire learns far less about who you’re connecting to. Great for privacy, famously inconvenient for inspection middleboxes, and that tension delayed enterprise rollouts for years. It explains most of the “TLS 1.3 broke our appliance” tickets of the early 2020s.

What to actually run

The 2026 baseline isn’t controversial: TLS 1.3 enabled and preferred, TLS 1.2 kept as the floor with a modern suite list (ECDHE key exchange, AES-GCM or ChaCha20), and TLS 1.0/1.1 refused outright. Those last two were formally deprecated by RFC 8996 in 2021, and every current browser dropped them back in 2020. Keeping 1.2 as the floor costs you nothing in security when it’s configured well, and it keeps the long tail of older clients and embedded devices working.

Adoption data says you’ll rarely need even that floor. Qualys SSL Pulse has tracked TLS 1.3 support climbing past the three-quarters mark across popular sites, and browsers have supported it universally since 2019. The stragglers are almost always B2B integrations and ancient Java runtimes. That’s an inventory problem, not a protocol one.

On the server side it’s usually a few lines. Nginx: ssl_protocols TLSv1.2 TLSv1.3; plus a sane cipher string for the 1.2 fallback (1.3 suites aren’t configurable, by design). Apache and HAProxy have the same two knobs, and so do the CDN dashboards. While you’re in there, add HSTS so returning browsers never even try plaintext; our HTTP headers checker grades that part of the config in one click.

Verifying the result

Trust, then verify from outside. Point our SSL checker at your host: it reports the negotiated protocol and cipher next to the certificate countdown, which catches the classic case of a load balancer fronting your beautifully configured backend with its own 2019-era settings. We’ve hit that one more than once. For the full matrix, openssl from any shell answers version by version: openssl s_client -connect host:443 -tls1_1 should fail, -tls1_3 should succeed.

One habit worth keeping: re-test after every infrastructure change. TLS termination has a way of moving (a new CDN here, a new ingress controller there) and every move resets your protocol configuration to whatever that layer’s defaults are. The defaults are better than they used to be. They’re still not your config.

What’s already arriving: post-quantum key exchange

The next chapter is being deployed on top of TLS 1.3, not as a TLS 1.4. The worry is “harvest now, decrypt later”: traffic recorded today could be decrypted decades from now by a quantum computer breaking the elliptic-curve key exchange. The countermeasure is hybrid key exchange, x25519 paired with ML-KEM (the NIST-standardized Kyber), so a session stays safe unless both problems fall. Chrome ships it on by default, and Cloudflare reports a large share of its TLS 1.3 traffic already negotiating post-quantum keys. OpenSSL 3.5 brought support to the server mainstream.

Two practical notes if you operate servers. First, hybrids ride on TLS 1.3’s key share mechanism, so a 1.2-only endpoint is locked out of the upgrade path entirely; honestly, that’s becoming the strongest argument for finishing your 1.3 rollout. Second, the bigger ClientHello (Kyber keys are chunky) has flushed out middleboxes and load balancers that assumed a hello fits in one packet, a bug class worth testing for before your users find it. The protocol keeps evolving. The operational lesson doesn’t: keep the floor modern, and the future arrives as a config change instead of a migration.

Frequently asked questions

Is TLS 1.2 insecure in 2026?

No. TLS 1.2 with modern cipher suites (AES-GCM or ChaCha20, ECDHE key exchange) is still solid, and every compliance framework we deal with accepts it. The scary stories belong to TLS 1.0/1.1, which RFC 8996 formally deprecated, or to TLS 1.2 dressed in legacy options like CBC suites and RSA key exchange. In our experience the problem is configuration, not version.

Does TLS 1.3 make my site measurably faster?

On new connections, yes: one round trip saved on every handshake. The gain scales with latency, so a user 100 ms away saves 100 ms on first connect, and mobile networks feel it most. Resumed connections are quick on both versions, and TLS 1.3 adds 0-RTT resumption for another saving if you accept its replay caveats.

What is 0-RTT and should I enable it?

Zero round trip resumption lets a returning client send application data in its very first packet. The catch: an attacker can replay that early data, so it's only safe for idempotent requests like GETs. We enable it on content sites, with the proxy restricting early data to safe methods, and skip it on APIs that mutate state.

Why can my old monitoring appliance not inspect TLS 1.3 traffic?

TLS 1.3 encrypts the certificate exchange and removed static RSA key exchange, which is exactly what passive middleboxes relied on to decrypt traffic with a copied private key. Inspection now means being an active proxy that terminates the session. That broke a generation of enterprise appliances and delayed plenty of TLS 1.3 rollouts; the protocol chose privacy on purpose.

How do I check which TLS version my server negotiates?

Our SSL checker reports the negotiated protocol and cipher for any host. From a terminal, openssl s_client -connect host:443 -tls1_3 (then -tls1_2 and -tls1_1) shows exactly which versions the server accepts. Aim for 1.3 preferred, 1.2 accepted, everything older refused.

Tags: articlehttpsperformancesecuritytls
Share199Tweet125
stephane

stephane

  • Trending
  • Comments
  • Latest
Answer card: Proton Lumo 2.0 is private by policy, not by locality. Saved history is locked so even Proton cannot read it, but the prompt is decrypted on a Proton EU server to answer it, then forgotten.

Proton Lumo 2.0 review: how private is it, really?

3 September 2026
The Agentic Coding section of the official Hy4 preview benchmark appendix published by Tencent, a table comparing Hy3 and Hy4 preview against DeepSeek V4 Pro 0813, Qwen 3.8 Max, GLM 5.3, Kimi K3, GPT 5.6 Sol and Claude Opus 5 across SWE-bench Multilingual, SWE-bench Pro, DeepSWE, three SWE Atlas tasks, SWE-Marathon, Terminal-Bench 2.1, NL2Repo-Bench, CyberGym, ProgramBench, PostTrainBench and Harbor-Index.

Tencent’s 770B Hy4 tops one benchmark row in 46

3 September 2026
Answer card: Qwen 3.7 Max is API-only and cannot run locally yet; the open Qwen models (Qwen 3.6 27B, qwen3:8b to 32b) run offline via Ollama.

Qwen 3.7 local: what you can actually run offline

22 June 2026
Answer card: JWTs are not encrypted, anyone can read them; the signature proves who issued the token, not who may read it.

Are JWTs encrypted? No, and the difference will bite you

0
Answer card: a random 8 character password falls in under 2 hours offline, while 16 random characters hold for 1.4 trillion years at the same speed.

How long does it take to crack a password in 2026?

0
Answer card: three DNS records decide if your mail lands or bounces; SPF lists allowed senders, DKIM signs messages, DMARC sets the failure policy.

SPF, DKIM and DMARC explained: the records your email needs

0
Answer card stating that OpenAI released the Agents API in public beta on 10 September 2026 with no separate fee, billed through model tokens, tool calls and hosted sandbox time, with a choice of OpenAI hosted, self hosted or partner sandboxes, US only data residency and no Zero Data Retention support.

OpenAI’s Agents API has no fee, no ZDR and a one hour sandbox clock

14 September 2026
Answer card: Sakana Fugu Max at $2 and $6 per million tokens, Fugu Ultra v2 unchanged at $5 and $30, and Sakana saying Ultra v2 scores without Fable 5 or GPT-6 Astra in its pool.

Fugu Max costs $2 and $6 while Fugu Ultra v2 runs without Fable 5

13 September 2026
Answer card stating that DeepSeek released DeepSeek-V4.1-Flash on 10 September 2026 as a 552 billion parameter mixture of experts model with a new causal encoder decoder architecture that activates 8 billion parameters on input and 16 billion on output, with native vision, a one million token context and MIT licensed weights, that the API model name is now deepseek-flash at 0.15 dollars per million input tokens and 0.60 dollars per million output tokens off peak, and that DeepSeek announced V4 Pro would be routed to V4.1-Flash from 14 September and reversed that on 11 September.

DeepSeek V4.1-Flash arrived, and the V4 Pro retirement lasted a day

12 September 2026
  • About
  • Contact
  • Privacy
  • Legal

Copyright © 2026 Stephane Cardon.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In
No Result
View All Result
  • Home
  • Articles
    • Security
    • Network
    • Dev
    • Sysadmin
    • SEO
    • Email & DNS
  • Tools
    • Network tools: free, fast, no signup
    • Security tools: free, fast, no signup
    • Developer tools: free, fast, no signup
    • Sysadmin tools: free, fast, no signup
    • SEO tools: free, fast, no signup
    • Email & DNS tools: free, fast, no signup
  • Download
  • About

Copyright © 2026 Stephane Cardon.